WordPress Security Crisis 2026:
Millions of Websites Exposed
Author
Eslam Abdullah
Date
Reading Time
4 Min Read
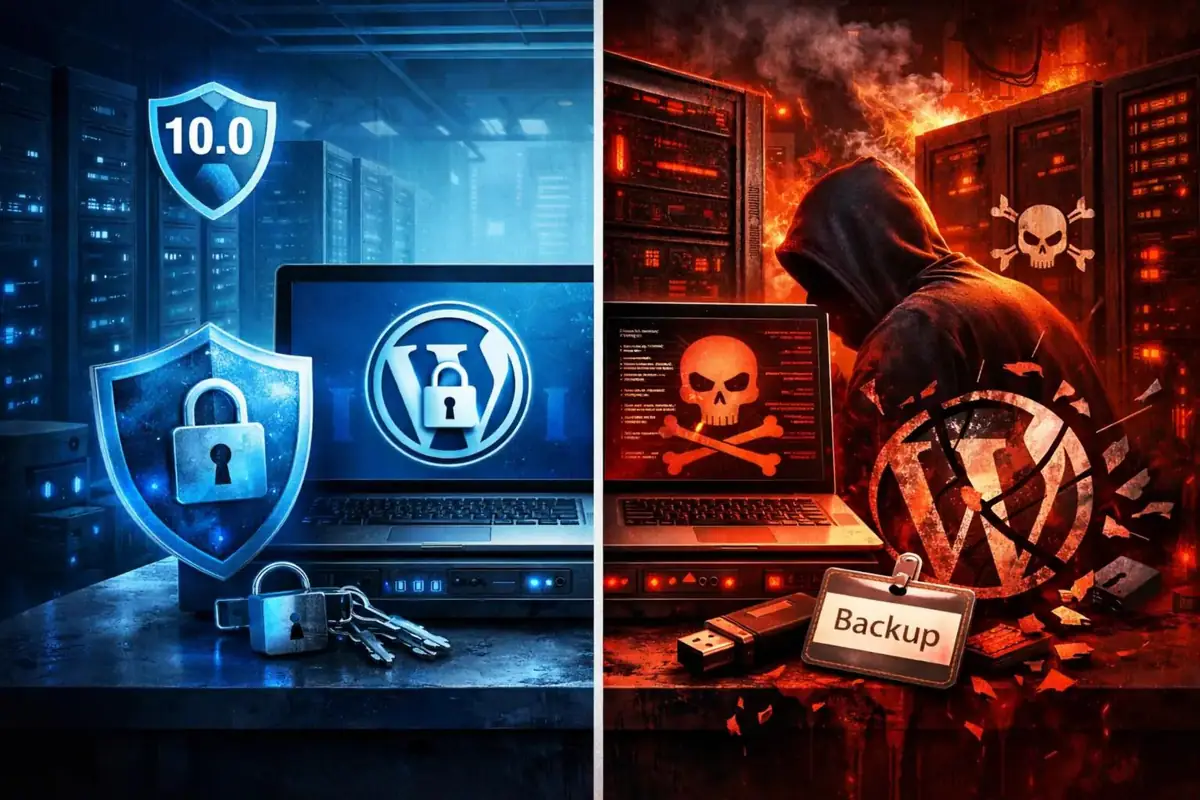
The WordPress ecosystem is facing one of its most serious cybersecurity waves in recent years after researchers disclosed dozens of high-severity vulnerabilities affecting widely used plugins and themes across millions of websites worldwide.
According to recent security intelligence reports, attackers are actively exploiting flaws in plugins such as Burst Statistics, MonsterInsights, Avada Builder, and Breeze Cache. Several of these vulnerabilities allow authentication bypass, arbitrary file uploads, privilege escalation, and remote code execution — enabling hackers to fully compromise websites without requiring valid administrator credentials.
Researchers also warned that many sites are being attacked only hours after public disclosure of new vulnerabilities, leaving little reaction time for administrators who fail to update quickly.
Escalating Threat Landscape
Additional reports from SolidWP and WPScan indicate that the overall number of WordPress vulnerabilities has dramatically increased in 2026, with hundreds of newly discovered flaws appearing every month. Many remain unpatched for days or weeks, increasing the risk of mass exploitation campaigns targeting outdated websites.
What You Should Do Immediately
Cybersecurity experts are urging website owners to take the following actions:
- Update all plugins and themes to their latest patched versions.
- Remove any unused or abandoned plugins.
- Enable Web Application Firewalls (WAF) to block malicious requests.
- Use multi-factor authentication (MFA) for administrative accounts.
- Monitor websites for suspicious login activity and unauthorized file uploads.
Industry analysts believe the growing complexity of WordPress attacks reflects a broader trend in cybercrime automation, where attackers rapidly weaponize newly disclosed vulnerabilities at scale.
🔗 Sources
- Wordfence Vulnerability Report
- WP Vanguard Security Roundup
- SolidWP Security Report